What I Built (In Plain English)
Merging code directly into production or clicking merge buttons without thorough testing leads to outages and security holes.
I created an automated operational prompt for Google Antigravity AI that takes any code changes, isolates them on a feature branch, runs an automated security scan (checking for secrets and vulnerabilities), opens a PR to develop, waits for CI checks to pass, and only then promotes and tags the release on master.
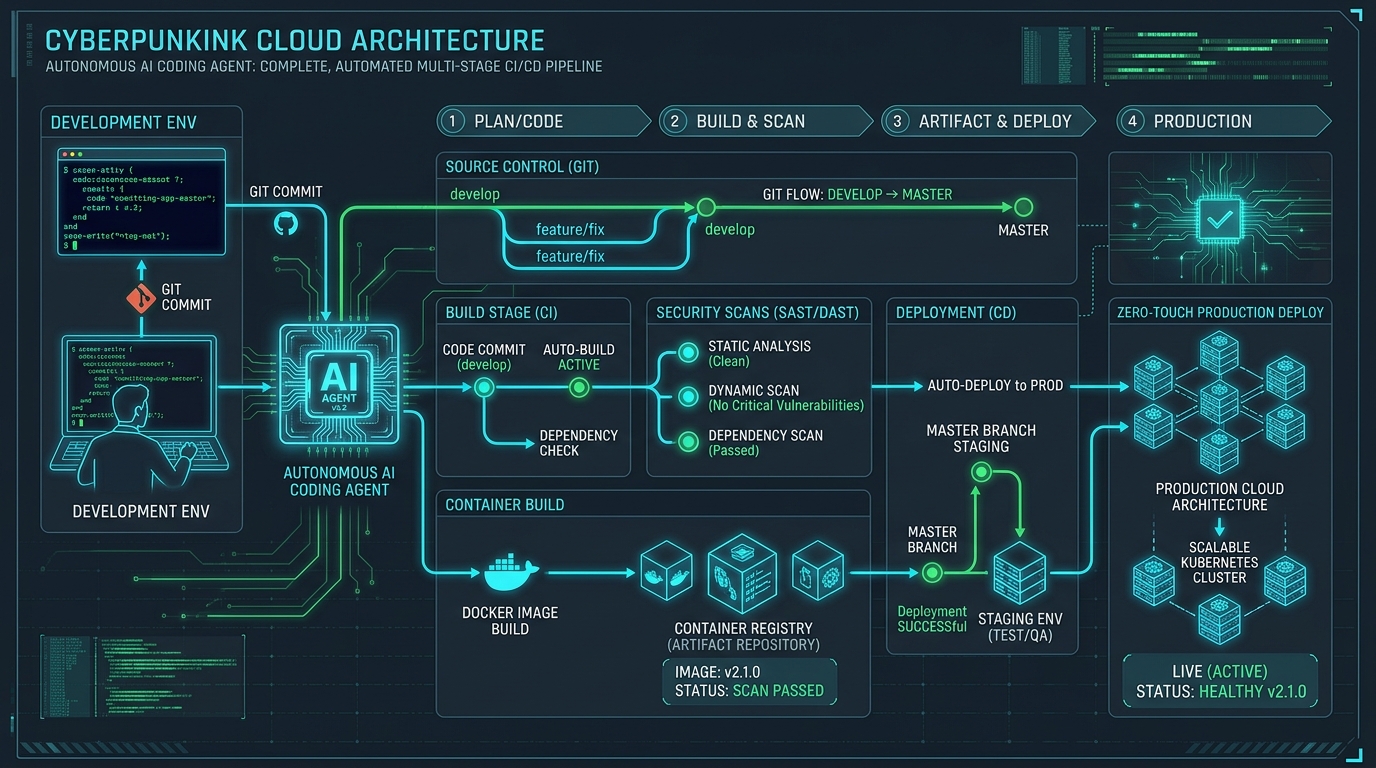
⚠️ Tech Ahead: The sections below outline branch isolation protocols, automated SAST security scans, staged CI gating, and semantic release tagging.
Architectural Objectives
- Isolation: Development occurs strictly on isolated branches (
feature/...orfix/...). - Security Gates: Static analysis scans for injection vulnerabilities, token leaks, and input sanitization before any merge.
- Staged Promotion: Changes merge to
develop, pass CI testing, and are then promoted tomasterwith automated semantic versioning and release tags.
The Operational Prompt
Run the full pull-request, security audit, and staged release pipeline for the current changes:

1. **Feature Branch & PR to Develop**:
   - Verify all local modifications are staged and committed with clean conventional commit messages.
   - Confirm branch isolation (`feature/...` or `fix/...`).
   - Push to origin and open a Pull Request targeting `develop`.

2. **Code & Cybersecurity Assessment**:
   - Perform a rigorous security and defect audit across all modified files:
     - Scan for injection risks (SQL, NoSQL, XSS, SSRF, command execution).
     - Verify no exposed secrets, auth tokens, or private credentials exist.
     - Validate input sanitization, authentication boundaries, and state race conditions.
     - Identify logic bugs, boundary edge cases, and type safety regressions.
   - If issues are detected, patch code, run unit tests (`npm test`), and push updates to the branch.

3. **CI/CD Gating & Develop Integration**:
   - Wait for remote CI/CD automated checks on the develop PR to pass green.
   - Once all checks pass, merge the PR into `develop`.

4. **Production PR & Tagged Release**:
   - Bump the release version semantically in `package.json` (patch/minor).
   - Open a Pull Request from `develop` into `master`.
   - Wait for all CI checks to pass green on the `master` PR.
   - Merge the PR into `master`.
   - Create and push an annotated git tag matching the release version (e.g. `vX.Y.Z`).
   - Monitor the deployment pipeline to completion and confirm zero regressions.
Verification Checklist
- Branch clean and rebased against
develop. - SAST/DAST checks: 0 high/critical vulnerabilities.
- Automated test suites (
npm test) pass 100%. - Production build (
npm run build) compiles with 0 errors. - GitHub Actions / CI pipeline green on
developandmaster. - Annotated Git release tag (
vX.Y.Z) pushed to remote.
— [ DISPATCH TRANSMISSION COMPLETE // END OF FILE ] —